See how it works.
Four screens, one conclusion.
This is the real Dela IEM console, in the order a security leader actually reasons: what identities do I have, how exposed am I, how would an attacker reach Domain Admin, and what do I fix first.
You cannot secure what nobody has counted.
Dela builds a complete, continuously refreshed inventory of every identity in your estate — users, service accounts, nested groups, delegations and privileged objects — across on-premises Active Directory and Entra ID in a single view. Most teams discover several hundred identities they did not know were active.
Complete hybrid identity inventory in under 10 minutes
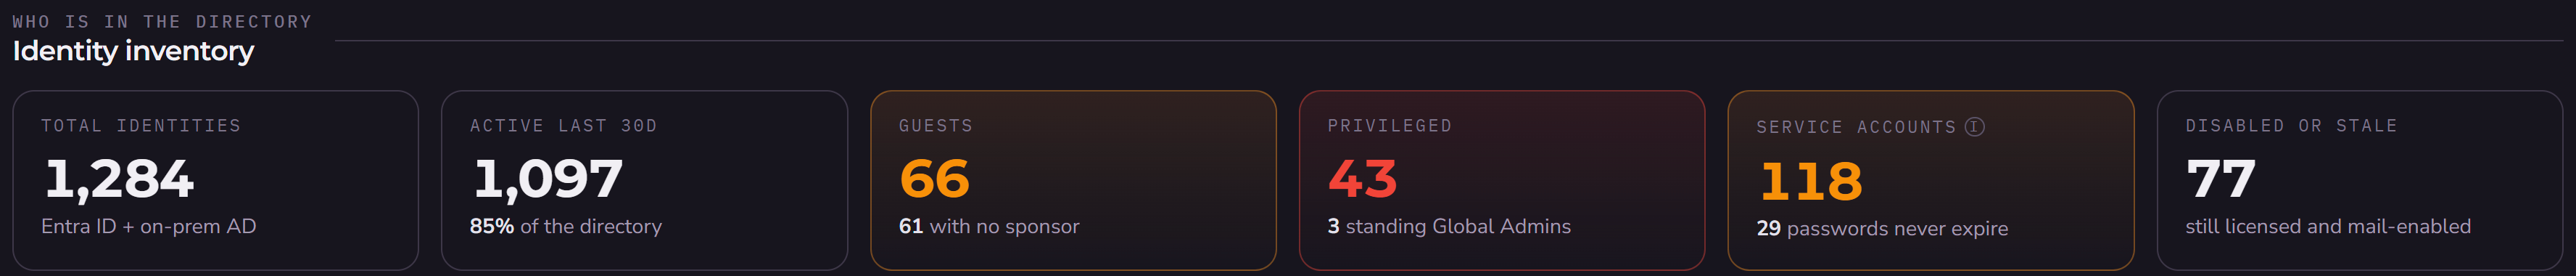
You cannot secure what nobody has counted.
Dela builds a complete, continuously refreshed inventory of every identity in your estate — users, service accounts, nested groups, delegations and privileged objects — across on-premises Active Directory and Entra ID in a single view. Most teams discover several hundred identities they did not know were active.
Complete hybrid identity inventory in under 10 minutes
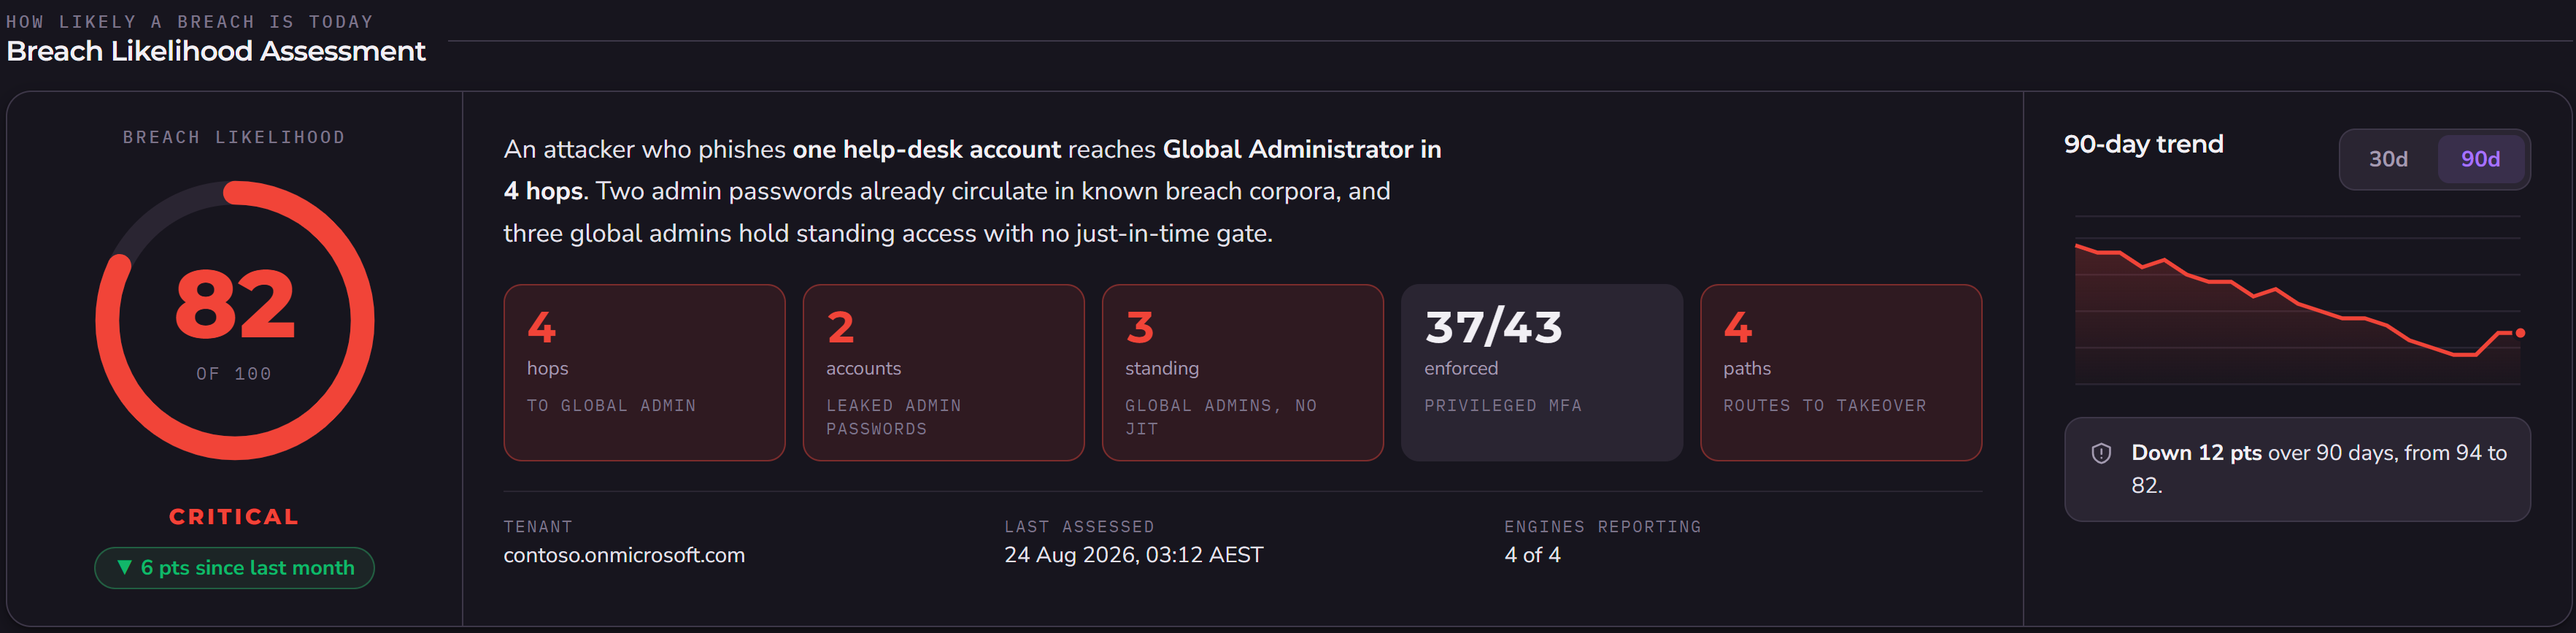
A number your board can actually act on.
Every exposure is scored against real exploitability, not generic CVSS severity. The result is a single breach likelihood figure with the specific conditions driving it — stale privileged accounts, weak delegation, MFA gaps, credential exposure — and how each one moves the number when it is closed.
Defensible risk posture for the board, the auditor and the insurer
See the route from ordinary user to Domain Admin.
Attackers do not think in findings lists, they think in paths. Dela maps every chain from a low-privilege foothold to Tier 0 — through group nesting, delegation, shadow admin rights and hybrid trust — and shows you the single choke points that break the most paths at once.
Break the chain at one hop instead of remediating a hundred findings
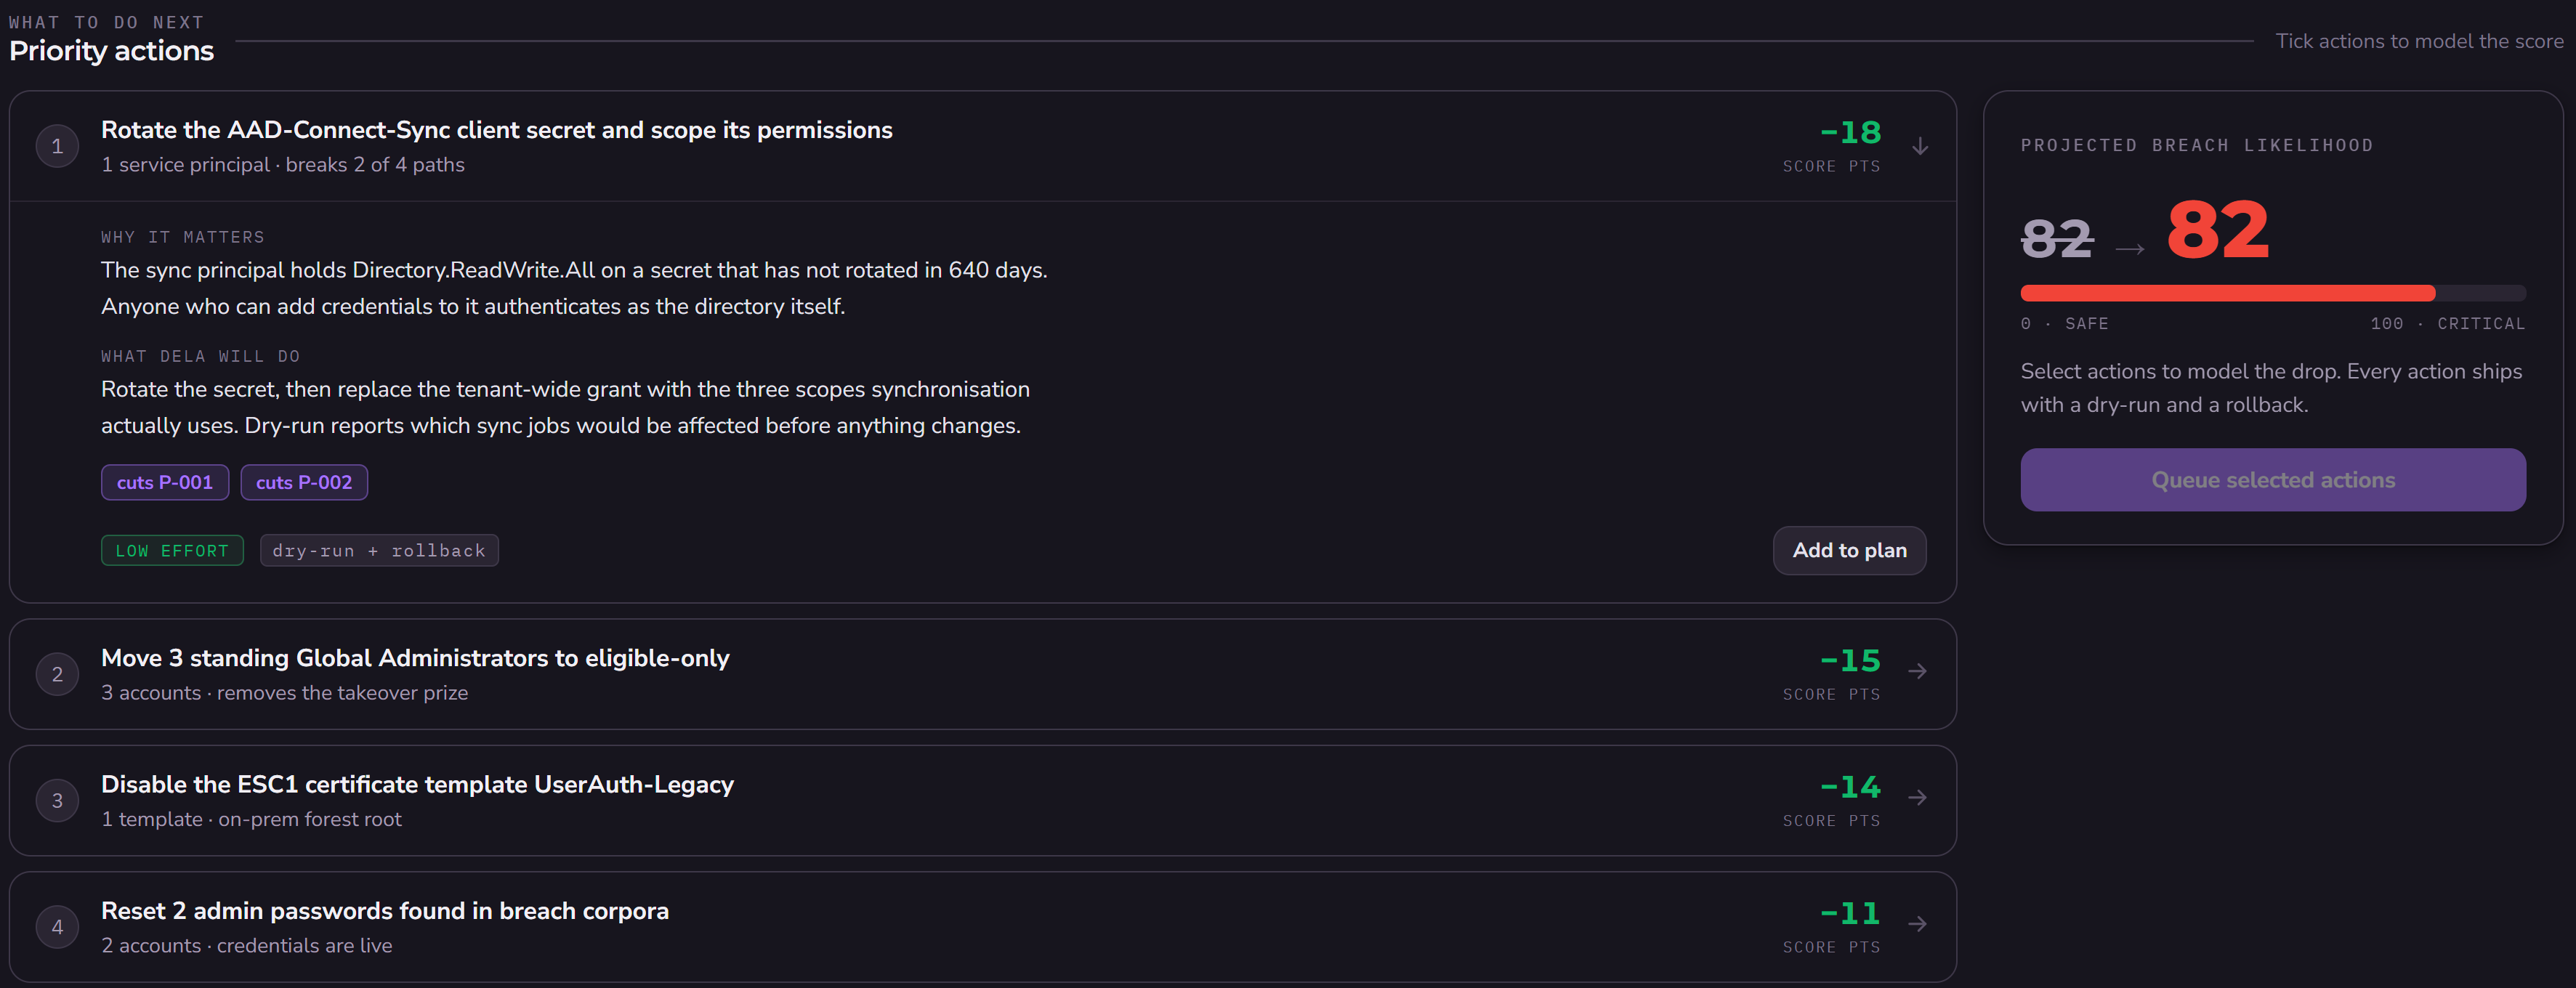
The short list that actually reduces risk.
Findings arrive ranked by blast radius and exploitability — not alphabetically, not by raw severity. Recurring hygiene issues are remediated automatically once you approve the policy. Your team works a prioritised queue that gets shorter, instead of a dashboard that never does.
Up to 90% identity risk reduction within the first 90 days
“We already have visibility.”
Visibility of accounts is not visibility of exposure. Dela shows which of those accounts an attacker can actually chain into privilege.
“We do not have time for another rollout.”
Read-only API connection, no agents, no scripts on domain controllers. First findings in roughly ten minutes.
“We do not have the people to action it.”
Findings arrive ranked by blast radius, and recurring hygiene issues remediate automatically once you approve the policy.
Now see it on your own environment.
The free Breach Likelihood Assessment runs against your live Active Directory and Entra ID — not a demo dataset. You get your actual exposure score, your actual attack paths, and the three actions that close the most risk.
Read-only · No agents · No change to production · Results in 60 minutes